Terris Recommends 16,400+ monthly visitors Business Services
11 Best Cybersecurity Companies in Singapore (August 2026)
My picks of the 11 best cybersecurity companies in Singapore for 2026, from CSA-licensed pen testing to managed SOC and compliance.
This guide is part of Terris Recommends, my researched, hands-on picks of the best local businesses and services in Singapore. Every recommendation is researched and ranked by me.
See all recommendationsChoosing a cybersecurity company in Singapore should start with a filter most buyers skip: are they licensed? Under the Cyber Security Agency's regime, the two highest-access services, penetration testing and managed security operations centre monitoring, are legally licensable, because a provider doing them gets deep access to your systems. So the first question is not who is cheapest, it is whether they hold a licence.
You can verify this yourself. The Cyber Security Agency sets the framework, and the Cybersecurity Services Regulation Office issues the licences and publishes the register of licensees. Once you have that trust filter, the practical decision is what you actually need: a penetration test to find weaknesses, managed detection and response to watch around the clock, or consulting for compliance. I will decode all of it, then give you my picks.
This is part of my Terris Recommends Business Services series. It pairs with my guide to IT support and managed services for SMEs.
Beyond the jargon, here is what actually matters when you choose a provider.
- CSA and CSRO licensing. Penetration testing and managed SOC monitoring are licensable services in Singapore. Check the provider on the CSRO licensed-service-providers register, and look for a licence number, since a provider getting deep access to your systems should be licensed.
- The right service. A penetration test finds and reports weaknesses. Managed detection and response, or MDR, watches your systems 24/7 and reacts to threats. Consulting and compliance covers PDPA, risk assessments and governance. Know which you need.
- Accreditation. For pen testing, CREST accreditation and certifications like OSCP signal genuine capability. For MDR, ask about the team, tooling and response process.
- SME versus enterprise fit. Some firms are built for banks and critical infrastructure, others for SMEs. Match the provider to your size and risk, and do not overbuy.
- Start with the basics. For most SMEs, the sensible order is cyber hygiene and staff awareness, then a penetration test, then an outsourced data protection officer, before a full managed SOC.
One tip: get a clearly scoped statement of work for any pen test, including what is in and out of scope, so you know exactly what was and was not tested.
| Firm | Focus | Best for |
|---|---|---|
| Ensign InfoSecurity | MDR, SOC, consulting | Larger organisations |
| ST Engineering | OT and critical infrastructure | Industrial and CII |
| Group-IB | Threat intelligence, MDR | Threat-led defence |
| Wizlynx | Pen testing, red team | Licensed VAPT |
| Swarmnetics | Pen testing, VAPT | Affordable testing |
| Privacy Ninja | Pen test plus DPO | SME PDPA compliance |
| Perennial | Pen testing | Licensed VAPT for SMEs |
| Netpluz | Managed SOC | SME managed security |
| Responsible Cyber | Third-party risk | Supply-chain risk |
| Singtel | Managed security | Telco-scale MSSP |
| Micrologic | SME managed security | SME budgets and grants |
Cost scales with scope and the service type. Here is what to expect in 2026.
| Service | Typical price | Good to know |
|---|---|---|
| Web-app penetration test | Around S$1,500 to S$3,000 | Basic single-application scope |
| Mid-size penetration test | Around S$5,000 to S$20,000 | Broader network and app scope |
| Enterprise red team | S$50,000 and up | Full adversarial simulation |
| Managed SOC or MDR | Monthly, priced by scope | 24/7 monitoring and response |
The scope, the number of systems and how deep the test goes drive the price far more than the logo. For an SME, a well-scoped web-app or network penetration test plus basic hygiene is usually the sensible starting spend, before committing to an ongoing managed SOC.
For an enterprise or a mid-sized company with real risk that wants a deep, end-to-end partner, it is the heavyweight choice. It is more than most small SMEs need, but for larger organisations it is a benchmark.
- Best for
- Larger organisations
- Best known for
- Asia's largest pure-play cybersecurity firm
- Focus
- MDR, SOC, consulting
- Website
- ensigninfosecurity.com
For a business in maritime, aviation, utilities or manufacturing, where OT security is a distinct and serious challenge, it is the specialist. For industrial and critical-infrastructure needs, it is my recommendation.
- Best for
- Industrial and CII
- Best known for
- Operational-technology security
- Focus
- OT and critical infrastructure
- Website
- stengg.com
For an organisation that wants defence informed by real-world threat actor intelligence, and a 24/7 incident-response capability, it is a strong, specialist choice. It suits those facing sophisticated, targeted threats.
- Best for
- Threat-led defence
- Best known for
- Threat-intelligence-driven detection and response
- Focus
- Threat intelligence and MDR
- Website
- group-ib.com
That combination of a CSA licence and CREST accreditation is exactly what you want to see for serious testing. For a business that needs rigorous, properly licensed VAPT, it is a top choice.
- Best known for
- Licensed, CREST-accredited penetration testing
- Focus
- Penetration testing and red team
- Licensing
- CSRO-licensed, CREST-accredited
- Website
- wizlynxgroup.com
That researcher-network approach makes quality testing more accessible on an SME budget. For a growing company that wants genuine testing without an enterprise price tag, it is a strong, practical choice.
- Best for
- Affordable, capable testing
- Best known for
- An elastic vetted-researcher testing model
- Focus
- Penetration testing and VAPT
- Website
- swarmnetics.com
With certifications like CEH and OSCP and hundreds of organisations served, it is well suited to SMEs. For a small business tackling PDPA and security together, it is my recommendation.
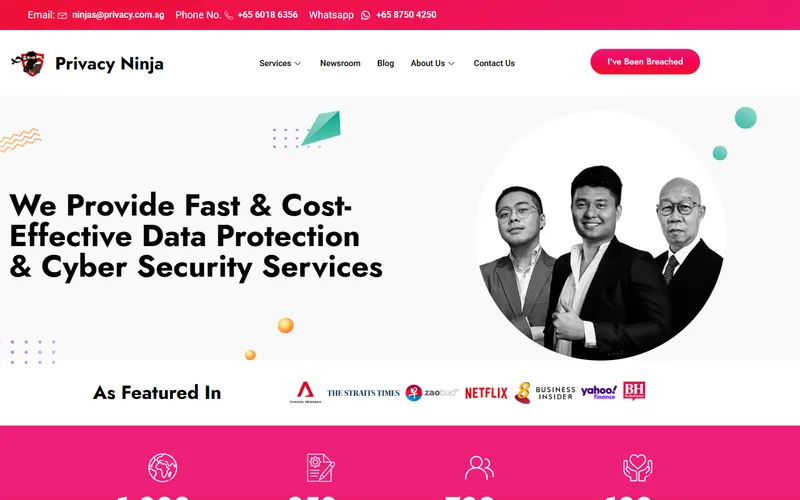
- Best known for
- Combining VAPT with PDPA compliance for SMEs
- Focus
- Pen testing plus outsourced DPO
- Licensing
- CSRO-licensed pen testing
- Website
- privacy.com.sg
That early licensing and solid credentials make it a dependable choice for a straightforward, properly licensed penetration test. For an SME that wants licensed testing from an experienced team, it is a strong option.
- Best known for
- An early-licensed penetration-testing specialist
- Focus
- Penetration testing
- Licensing
- CSA-licensed since 2022
- Website
- perennialconsultancy.com
That managed-services bundle, spanning both network and security, suits small and mid-market businesses that want it handled. For an SME wanting ongoing monitoring rather than a one-off test, it is a strong choice.
- Best for
- SME managed security
- Best known for
- Managed security bundled with network services
- Focus
- Managed SOC and security
- Website
- netpluz.asia
As supply-chain attacks rise, that focus is increasingly important. For a company that wants to get on top of third-party risk alongside its own defences, it is a forward-looking, specialist choice.
- Best for
- Vendor risk management
- Best known for
- AI-driven third-party risk management
- Focus
- Third-party and supply-chain risk
- Website
- responsible-cyber.com
For a company that values scale, uptime and the ability to combine security with its network under one vendor, it is a solid enterprise-grade choice. It is a safe pair of hands for managed security.
- Best for
- Telco-scale managed security
- Best known for
- A one-stop MSSP with global SOC coverage
- Focus
- Managed security services
- Website
- singtel.com
That combination of enterprise-grade security at SME pricing plus grant help makes real protection accessible to smaller companies. For a small business starting its security journey affordably, it is a practical choice.
- Best for
- SME budgets and grants
- Best known for
- Enterprise-grade security at SME pricing
- Focus
- SME managed security
- Website
- micrologic.com.sg
I looked at CSA and CSRO licensing for the licensable services, accreditations like CREST, the specific service focus, SME versus enterprise fit, and reputation. I deliberately spread the list across pen-testing specialists, managed SOC and MDR providers, compliance and third-party-risk firms, and SME-friendly options, because the right provider depends entirely on what you need.
Details are checked when I publish and revisited as things change. Always verify a provider on the CSRO licensed-service-providers register for licensable services, ask for a scoped statement of work, and start with the basics before buying a full SOC.
For certain services, yes. Under the Cyber Security Agency regime, penetration testing and managed security operations centre monitoring are licensable services, because providers delivering them gain deep access to client systems. Firms offering these must hold a licence issued by the Cybersecurity Services Regulation Office. Other services, like general consulting or awareness training, are not licensed. So when engaging a provider for a pen test or managed SOC, check that they are licensed by looking them up on the CSRO licensed-service-providers register, and ask for their licence number.
A SOC, or security operations centre, is a team and facility that monitors your systems for threats. An MSSP, or managed security service provider, is a company that runs security services for you, which may include operating a SOC on your behalf. MDR, or managed detection and response, is a specific service that combines monitoring with active threat hunting and response, going beyond alerting to actually contain threats. In short, a SOC is the capability, an MSSP is the provider, and MDR is a proactive service that detects and responds rather than just watching. For most SMEs, MDR from a good provider is the practical way to get 24/7 protection.
For an SME, the best provider depends on your immediate need. If you need a penetration test, Swarmnetics and Perennial offer capable, licensed testing at accessible prices, and Privacy Ninja pairs testing with PDPA compliance. For ongoing monitoring, Netpluz and Micrologic offer SME-friendly managed security. Most small businesses should start with cyber hygiene and staff awareness, then a penetration test and an outsourced data protection officer, before committing to a full managed SOC. Match the spend to your actual risk rather than buying enterprise services you do not yet need.
Check the Cybersecurity Services Regulation Office register of licensed service providers, which lists firms licensed to provide penetration testing and managed security operations centre services. You can also ask the provider directly for their licence number, which follows a standard format, and cross-check it. This matters because these are the two services where a provider gains deep access to your systems, so licensing is a genuine trust signal. If a firm offering pen testing or managed SOC cannot show a valid CSRO licence, treat that as a red flag and look elsewhere.
A company shortlisting cybersecurity companies in Singapore will look you up before anyone speaks to you, often several people independently.
They want to see relevant work, the certifications that apply, and some sign you have handled a company their size. B2B sites tend to be heavy on adjectives and light on proof, and that is the gap. I build websites for Singapore B2B firms that lead with the evidence, and I run the SEO so you show up for the specific searches procurement actually types.
If most of your pipeline is referral and you want inbound to pull its weight, tell me what you sell and I will give you a straight read.
The best cybersecurity company in Singapore for you is a licensed one matched to your actual need, so use the CSRO register as your trust filter, then choose by service: pen testing to find weaknesses, MDR to watch around the clock, or consulting for compliance. Wizlynx and Swarmnetics lead for testing, Ensign and Netpluz for managed security, and Micrologic for SMEs. Start with the basics before buying a full SOC.
Good security is not about buying the most, it is about buying the right things in the right order from a provider you can verify.
For everyday support, patching and helpdesk work, a security vendor is usually the wrong shape of supplier. My guide to the best IT support and managed services in Singapore covers that tier, and my company incorporation guide is the place to begin if the business is brand new.
If you run a technology or professional-services business and your website is not bringing in enquiries, that is what I do. I design websites for businesses across Singapore. Get in touch for a free consultation.